Every signal located.
Every incident owned.

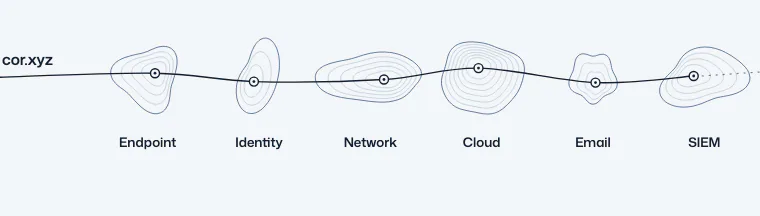
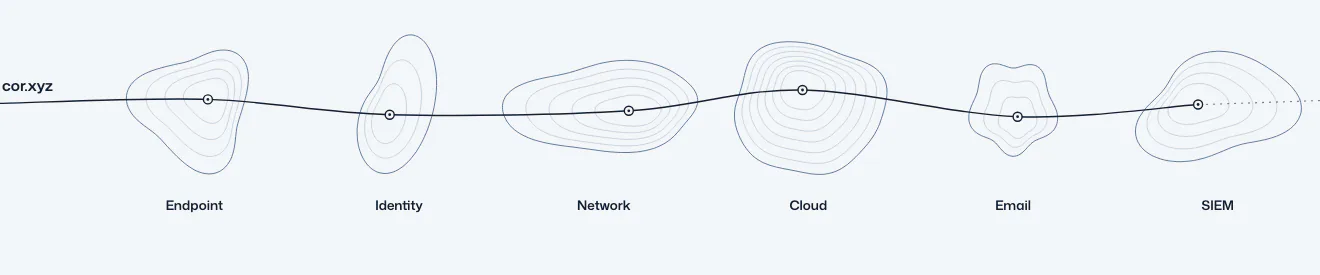
cor.xyz connects the security tools you already run, gives every signal its context, acts under the policy you set and turns each incident into one storyline. Governed agents carry the repeatable work. Our specialists stay accountable, 24×7. Your data stays where you decide.

Founded in Dubai in 2015.

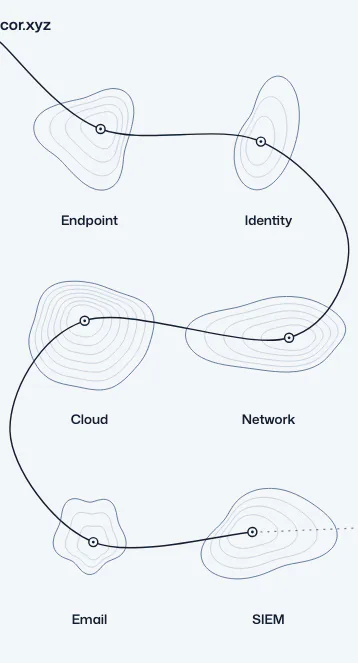
Map key
  • Asset
  • Storyline
  • Detection awaiting a decision
Dubai Internet City 25.10° N 55.16° E

Alerts compound. Humans don't.

Every tool, identity and cloud account you add produces more signal, and it never stops. Skilled analysts spend their shifts rebuilding the same context by hand: who owns this asset, what matters to the business, what the last investigation found. Then the shift changes and the next team starts again. Another tool rarely closes that gap. Usually it widens it.

SignalAnalyst capacityTimeThe work between the tools
Illustrative. No scale implied.
  • Signal grows without limit.

    Endpoint, identity, cloud, network and SaaS each raise their own alerts and exceptions. The estate never gets simpler.

  • Context is rebuilt every time.

    The same questions are answered again for every alert and every shift.

  • The work falls between the tools.

    Evidence lives in one system, the decision in another and the action in a third.

The work between the tools is the work that matters. In 2017 we started turning it into software.

It doesn't compete with your tools. It completes them.

cor.xyz is a cyberdefense platform with Managed Cyberdefense built in. It runs across the security technologies you have already chosen, from any vendor, on-premises, in the cloud or both. It carries the operating work between them: retrieving evidence, connecting related events, deciding what matters and coordinating the response. One platform, one view, one accountable relationship.

  • Coordinated operations.

    Work across your connected tools runs through one operating relationship, so no incident has to be pieced back together across disconnected dashboards.

  • Understanding specific to you.

    Investigations use your assets, identities, privileges, approved exceptions and history. An unusual login means something different on a privileged account.

  • Freedom of technology choice.

    Change vendors on your terms. Operations continue across the change, within supported integrations.

  • Someone accountable for the outcome.

    Platform execution plus specialists with agreed response authority, accountable for the incident and not just the alert.

Works across Microsoft, CrowdStrike, SentinelOne, Palo Alto Networks, Okta and others. No rip-and-replace. No proprietary lock-in.

Explore the platform

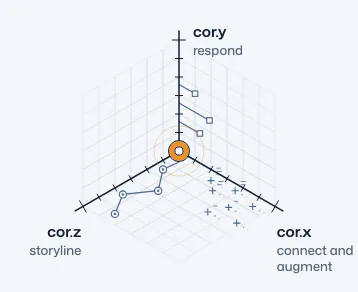
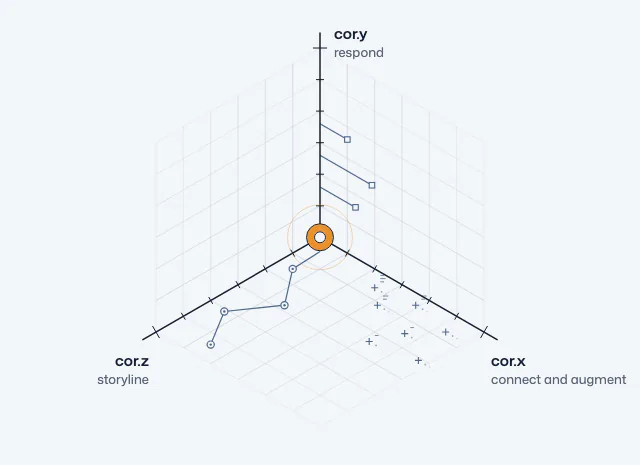
Three coordinates for every incident.

Three axes that work as one. Governed agents connect and augment every signal, respond under your policy, and turn each incident into one storyline.

cor.x connect and augment

anything. anywhere.

Every source connected. Every signal given its context.

cor.x connects the security technologies you run, on-premises, in the cloud or both, through a library of thousands of connectors and new ones built for your technology. Agents then augment each signal: they enrich it, read it against your client security data model and correlate it with related activity, with detections mapped to MITRE ATT&CK. By the time a decision is needed, the context is already there.

cor.y respond

act with precision.

From detection to decisive action, inside your policy.

Agents act on what cor.x has established. They block indicators, isolate assets, revoke sessions and open tickets across native and third-party controls. Pre-authorized actions run on their own, consequential ones wait for approval, and prohibited ones never run. Every trigger, action and validation step is logged as evidence for audit.

cor.z storyline

understand the story.

See the story behind the signal.

Related detections, and the actions taken on them, are chained into one live storyline, read against your own assets, identities and history. It shows who, how and why in a single narrative that your analysts, your board and your regulator can all follow.

Also on the platform: corIQ, Analytics & Insights, Threat Advisories, Asset & Identity Discovery, corEQ, Dashboard & Control, and Mobile Access with the cor.one app for security leaders on the move.

See cor.x, cor.y and cor.z in detail

An unusual privileged login, end to end.

This illustrative workflow shows what happens between the first signal and a closed incident, with no queue and no handover in between.

  1. Evidence. A privileged account signs in somewhere unusual. cor.xyz pulls evidence from the connected tools: identity provider, endpoint, VPN and cloud audit logs.

  2. Context. Agents read the account against the client security data model. It links the account to exposed assets, to its privileges and to its past activity, including an earlier incident with the same pattern.

  3. Hypothesis. An agent builds an incident hypothesis and a response recommendation, with the evidence attached and the reasoning recorded.

  4. Containment. Pre-authorized actions run at once: the session is revoked and the indicator is blocked. Anything more consequential waits for your approval or a specialist's.

  5. Storyline. The incident closes as one narrative with a full audit record, and the detection logic is updated from what was learned.

It runs the same way at 3 a.m. as at 3 p.m.

Illustrative workflow. In practice, the steps follow your estate, your connected sources and your response policy.

See how agents and people share the work

Agents do the work.
You keep the authority.

Specialized agents read every detection against your whole environment and then close it, stage it or escalate it, with the reasoning recorded. They contain as well as recommend. Your analysts and ours become the escalation route, not the assembly line.

  • Review. Each detection is read against your assets, identities and history, never in isolation.
  • Cancel. Known noise is suppressed for you, with the reason kept so it isn't argued again every shift.
  • Decide. Stage, release or escalate, with the reasoning recorded for audit.
  • Contain. Block, isolate and revoke against approved playbooks. Executed, not just suggested.
  • Evolve. Detection logic and rule health improve from what the platform sees across your estate.

Your response policy, in three tiers

Pre-authorized.

Actions you approved in advance run automatically: block an indicator, isolate an endpoint, revoke a session, suppress known-benign noise. Logged and reversible.

Approval-required.

Consequential actions are staged with evidence and a recommendation, then wait for your approval or a specialist's. Approval is one tap in cor.one.

Illustrative cor.one screen. The incident "Unusual privileged sign-in": revoking the session and blocking the indicator are pre-authorized and have run. Isolating the affected host is staged and waits for approval with Face ID.

Prohibited.

Actions you have ruled out never run, whatever an agent concludes. Policy sets the boundary, not the model.

Every action carries an audit trail. That is what lets a regulated organization sign off on automation.

Independently audited against SOC 2. Report available under NDA.

Read how response policy works

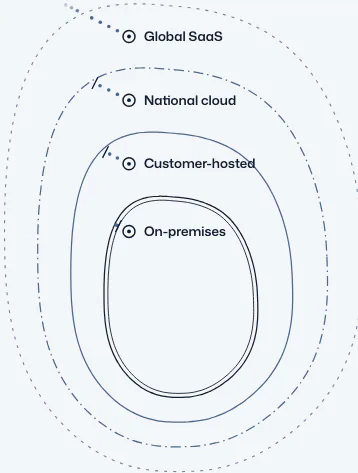
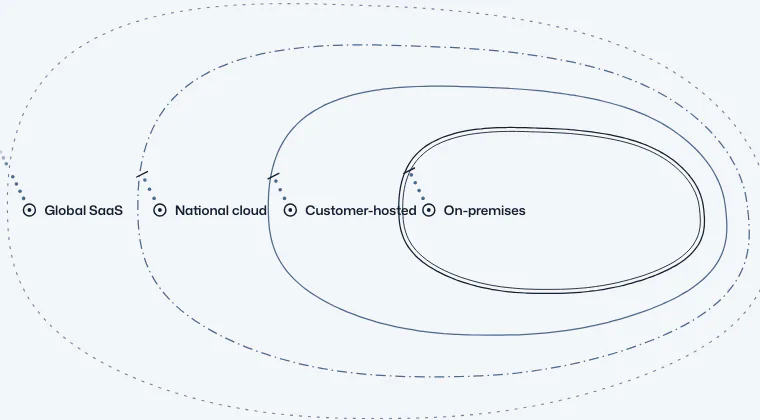
Your data. Your borders. Your rules.

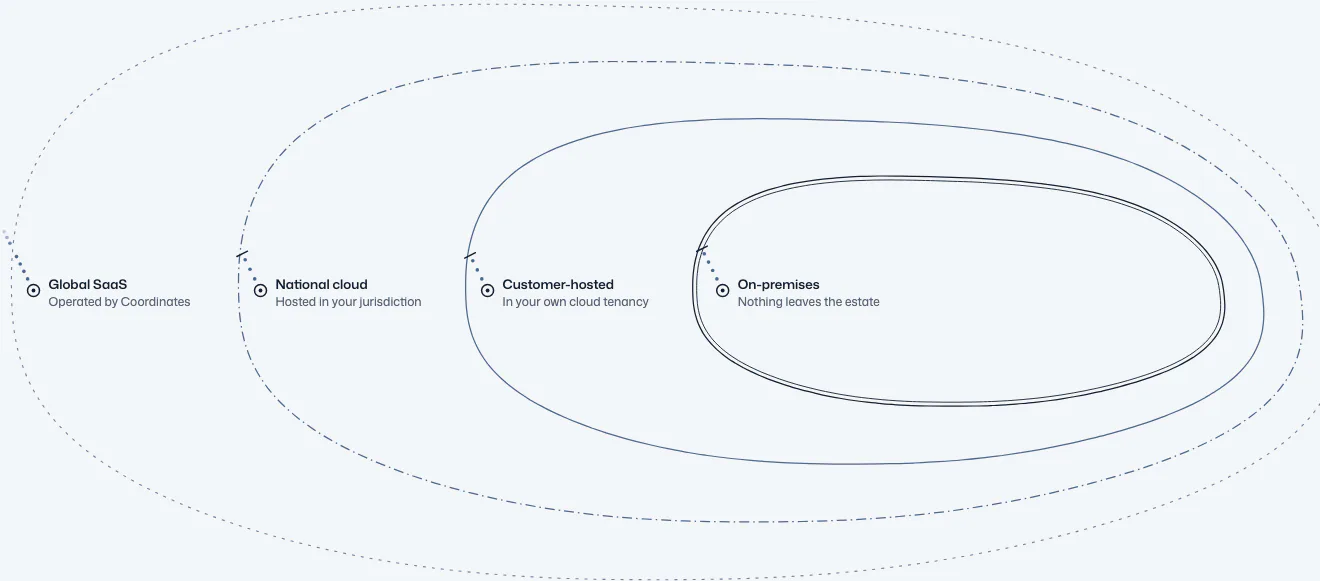
Gulf enterprises and public institutions increasingly need their security data and response authority to stay in-country. cor.xyz was designed for that. It runs where your architecture and data requirements say it should, and your policy decides what is processed where, and by whom.

  1. Global SaaS.

    Operated by Coordinates. The fastest path for organizations without residency constraints.

  2. National cloud.

    Platform and data hosted within your national cloud jurisdiction.

  3. Customer-hosted.

    cor.xyz runs inside your own cloud tenancy, under your own controls.

  4. On-premises.

    Fully contained in your own data center. Nothing leaves the estate.

  • Full data residency. Telemetry, context and evidence stay where you require.
  • Policy-based routing. You define what data leaves or stays, down to individual event types.
  • Federated intelligence. Detection content improves across clients, while each client's context stays its own.
  • Edge analytics. Analysis runs close to the data when the data cannot move.

Three questions we hear in every first meeting.

Why not our endpoint vendor's own MDR?

Because it defends one ecosystem. cor.xyz defends the whole estate, including the identity, cloud and network tools that vendor does not own, and the tools you will buy next.

What happens when we change SIEM?

Operationally, nothing. Your security data model, workflows and history stay with you. The new source is connected and the operation continues, within supported integrations.

Who is accountable at 3 a.m.?

We are. Agents adjudicate and contain under the policy you agreed, and UAE-based specialists govern escalation and every consequential decision, 24×7.

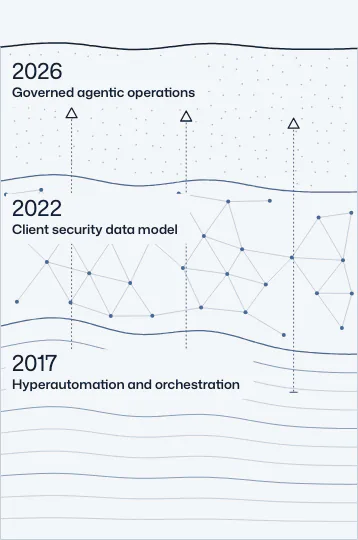
Execution first. Then context. Then agents that can use both.

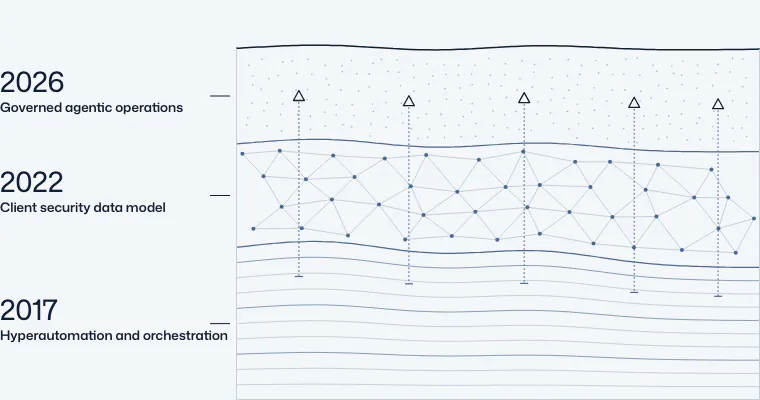
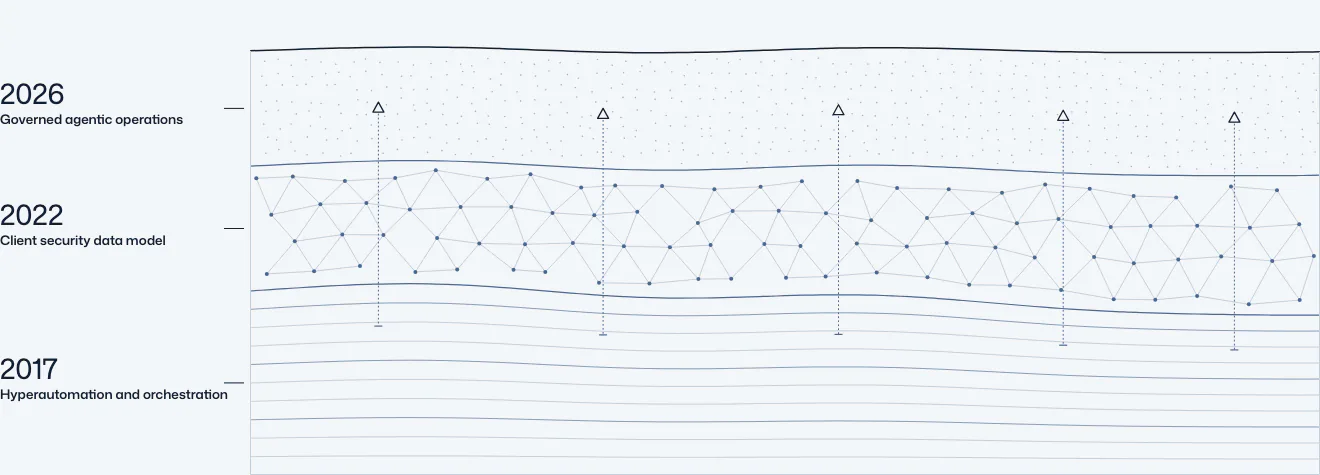
Agents are the visible layer. Beneath them are foundations built in sequence since 2017, and every one of them is still at work.

  1. 2017

    Hyperautomation and orchestration

    We turned repeatable cyberdefense work into software: workflows that retrieve evidence, enrich signals and carry out approved actions across the estate.

    What changed: we could act across a client's whole estate through software.

  2. 2022

    Client security data model

    Execution produces evidence. We connected that evidence into a persistent model of each client's environment: assets, identities, privileges, vulnerabilities, incidents, approved exceptions and response outcomes.

    What changed: execution gained a memory.

  3. 2026

    Governed agentic operations

    Specialized agents reason over that model and act through the orchestration foundation, while specialists validate findings and govern the consequences.

    What changed: agents with context and a way to act, under human authority.

Anyone can add a model to a security product. What matters is what the model works from.

Read the Coordinates story

Talk to the people who operate it.

A briefing is a working session with our specialists. We take cor.xyz through your tools, your residency requirements and your response policy, and answer the three questions above for your estate.

We use your details only to arrange the briefing. See our privacy notice.